


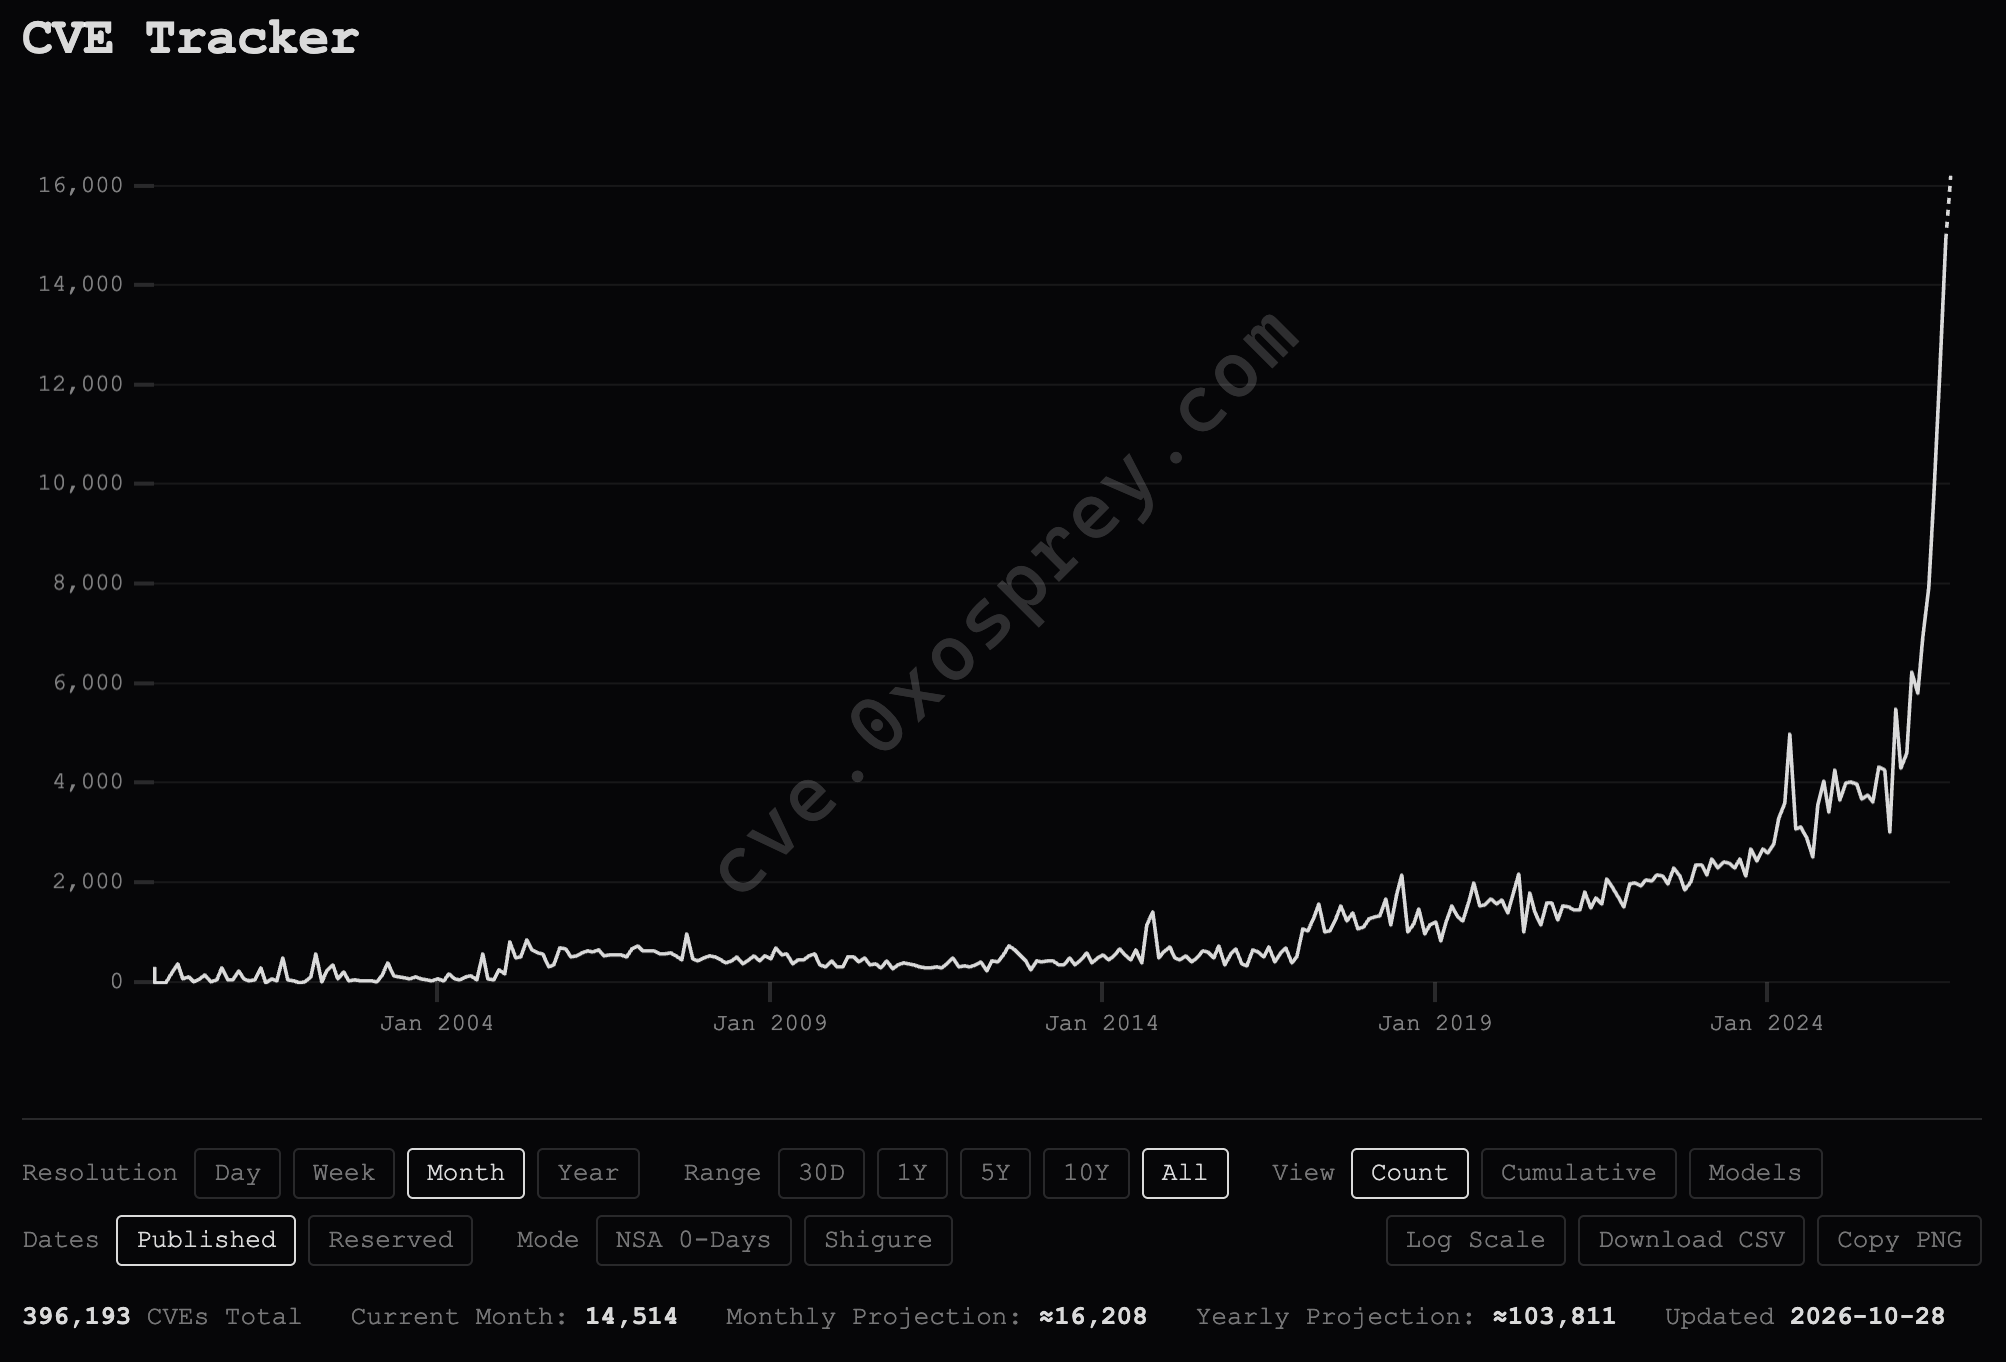
Last week coined the term “Black October“ after an onslaught of critical vulnerability disclosures, including PHP2Shell and a long-standing GitLab bug, signified the moment when the cyber risks of AI models started to materialize. It seemed like the news cycle had stabilized a bit when I started writing this, but then there was news about another major crypto security incident at Binance. The crypto industry has a very long history of hacks, so it’s not the best industry to indicate vulnerabilities translating into new societal harm. Still, we are very much still living through the implications of this transition.
The best guess for what is happening in the cybersecurity space is that the behind the scenes work has only accelerated, bringing more people and resources in to try and patch the internet — the Wall Street Journal reported that cyber first responders are strained, which seems like the system working. We’re living through this plot of an exponential rise in vulnerabilities, which will take a long time to level off at the top of the sigmoid.
A few weeks ago, before the rapid acceleration in vulnerability disclosures and the uptick in reported hacks, I wrote the following take. It’s been getting a pretty consistent barrage of feedback, some hopeless dunk attempts and some reasonable discussion, so I wanted to unpack…
Source: Interconnects — Read the full article on the original site ↗